
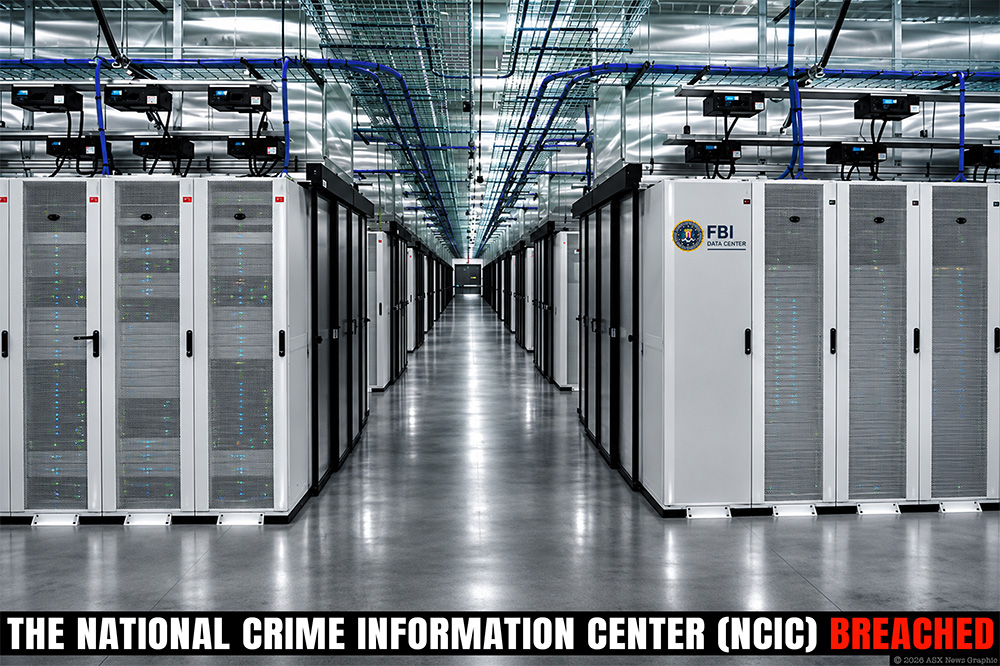
Another major component of America’s national security infrastructure has reportedly fallen victim to unauthorized digital intrusion. On November 20, 2026, CNN reported that the Federal Bureau of Investigation was investigating an apparent breach of its National Crime Information Center (NCIC), one of the most operationally important criminal justice information systems in the United States. Subsequent reporting by the Associated Press, Reuters, and Fox News has reinforced concerns surrounding the incident, which represents the latest in a succession of cybersecurity incidents and technological disruptions affecting both governmental and commercial infrastructure.
The significance of the reported intrusion extends considerably beyond the FBI itself. Unlike a conventional commercial database containing customer information, the NCIC supports operational decisions made by law enforcement personnel throughout the United States. Its integrity directly affects the safety of police officers, the protection of innocent citizens, the apprehension of dangerous criminals, and the administration of criminal justice.
The incident comes at a particularly troubling moment. Recent disruptions affecting aviation, banking, government communications, and national security systems have exposed the extraordinary degree to which modern civilization depends upon the continuous availability and accuracy of interconnected digital infrastructure. Whether these failures result from hostile activity, software deficiencies, maintenance procedures, or administrative failures, their operational consequences illuminate a common vulnerability.
The Digital Nervous System of American Law Enforcement
Established in 1967, the National Crime Information Center transformed American law enforcement by creating a centralized electronic infrastructure through which criminal justice agencies could rapidly exchange information across jurisdictional boundaries. Before the development of such systems, obtaining information from distant law enforcement agencies frequently required telephone calls, manual record searches, and substantial administrative coordination.
Today, NCIC provides authorized agencies with access to information concerning wanted individuals, missing persons, stolen vehicles, stolen firearms, protection orders, registered sex offenders, and other criminal justice matters. Its capabilities allow an officer conducting a routine traffic stop in Florida to discover that an individual encountered during that stop is wanted by authorities in another state.
For generations of American law enforcement personnel, NCIC has become an integral component of daily police operations. Its availability and reliability are particularly important during encounters in which officers must make consequential decisions with limited time and incomplete information.
Consequently, unauthorized access to this infrastructure presents possibilities considerably more disturbing than the disclosure of personal information. It raises fundamental questions about the reliability of the information upon which public safety decisions depend.
When Information Integrity Becomes a Matter of Life and Death
Cybersecurity traditionally encompasses three principal objectives: confidentiality, integrity, and availability. Confidentiality concerns the protection of information against unauthorized disclosure. Integrity concerns its accuracy and protection against unauthorized modification. Availability concerns the ability of authorized personnel to access that information when required.
Within criminal justice infrastructure, the consequences of compromised information integrity can be particularly severe. A successfully manipulated criminal justice record could theoretically cause a dangerous fugitive to appear free of outstanding warrants. Conversely, the fraudulent insertion of criminal justice information could expose an innocent individual to wrongful detention, arrest, or an unnecessarily dangerous confrontation with law enforcement personnel.
Similarly, unauthorized modification of information concerning stolen vehicles, protection orders, or missing persons could obstruct legitimate investigations and compromise public safety. The ability to corrupt information without producing an immediately recognizable system failure represents an especially dangerous category of cybersecurity threat.
There is presently no public evidence establishing that NCIC records were altered during the reported November intrusion. However, the distinction between unauthorized access and unauthorized modification will be among the most consequential elements in determining the operational severity of the incident.
A database that becomes temporarily unavailable announces its failure. A database that continues functioning while providing corrupted information may conceal its failure from the very personnel entrusted with acting upon it.
The President Responds
During a November 21 telephone interview with Fox News host Kayleigh McEnany, President Donald Trump acknowledged that he had recently learned of the reported intrusion and expressed dissatisfaction with the development. Trump subsequently suggested that the incident might result in the disclosure of information concerning previous political investigations and his allegations of electoral misconduct.
The president’s remarks provided no technical details concerning the intrusion, the identity of the responsible parties, the nature of the information potentially exposed, or the extent to which the operational integrity of NCIC might have been affected.
As of November 22, the FBI had not publicly disclosed a comprehensive account of the incident. The precise intrusion mechanism, duration of unauthorized access, affected components, potential extraction of information, and possibility of unauthorized record modification had not been established publicly.
A Troubling History of FBI Security Incidents
The reported NCIC compromise is not the first cybersecurity incident involving the FBI during 2026. In March, the bureau disclosed that it was examining suspicious activity involving an internal system associated with sensitive investigative and surveillance information.
In September, the digital extortion organization known as ShinyHunters was implicated in an intrusion involving the FBI’s recruitment infrastructure. The attackers claimed to have acquired extensive personal information concerning bureau employees and applicants. Subsequent criminal investigations resulted in arrests involving individuals suspected of participating in activities associated with the organization.
The November incident represents a potentially different category of exposure. Whereas recruitment information can provide opportunities for identity theft, extortion, targeting of personnel, and intelligence collection, interference with operational criminal justice infrastructure introduces the additional possibility of directly affecting law enforcement activities.
No publicly established evidence currently identifies ShinyHunters as responsible for the apparent NCIC intrusion. Nevertheless, repeated security incidents involving different components of the nation’s principal federal investigative agency raise legitimate questions concerning the effectiveness of existing cybersecurity defenses and the resilience of the infrastructure they are intended to protect.
Beyond the FBI: An Infrastructure Under Increasing Pressure
The reported intrusion follows a succession of technological disruptions that have attracted considerable public attention during November 2026. These incidents have involved governmental and commercial systems whose uninterrupted operation is essential to modern economic activity, transportation, communications, and national security.
Recent reports have included disruptions affecting Federal Aviation Administration operations, the National Security Agency’s internal network, banking services, and Microsoft’s global technology infrastructure. An additional cybersecurity incident involving a United States Department of Agriculture system used in agricultural payment operations was reported during the same week.
Reuters reported that recent aviation disruptions affected more than 18,000 flights, illustrating how technological failures can rapidly extend beyond the organization in which they originate. Government officials have attributed several recent outages to system upgrades and vulnerability remediation rather than deliberate cyberattacks.
The incidents have not been demonstrated to share a common perpetrator, technical cause, or coordinated operational objective. Nevertheless, evaluating them collectively remains important from an infrastructure reliability perspective. Each represents an additional demonstration of the operational consequences that can emerge when essential technological systems become compromised, degraded, or unavailable.
The broader vulnerability is not dependent upon proving that every incident originated from hostile activity. Infrastructure can be rendered ineffective through deliberate attack, defective software, incompatible updates, inadequate system architecture, administrative error, or failures of supporting services. From the perspective of the individuals and organizations dependent upon that infrastructure, the operational consequences may be remarkably similar.
The Dangerous Concentration of Technical Dependency
Modern civilization has progressively consolidated essential capabilities within increasingly sophisticated digital ecosystems. Governments, commercial enterprises, transportation networks, hospitals, financial institutions, utilities, and emergency services routinely depend upon centralized databases, communications infrastructure, cloud computing services, and interconnected authentication systems.
These arrangements provide extraordinary operational efficiencies. Information can be transferred almost instantaneously, administrative functions can be automated, and organizations separated by thousands of miles can coordinate their activities in real time. Yet the same integration that produces those efficiencies can introduce common points of dependency through which localized failures propagate across organizational and geographical boundaries.
An interruption involving a widely utilized authentication service can prevent access to otherwise functional applications. A defective software update can simultaneously affect thousands of geographically dispersed computers. A communications failure can isolate organizations from essential information even when their internal systems remain intact.
Such dependencies create opportunities for cascading failure, a phenomenon familiar to researchers examining complex technological systems. The initial failure of one component can impose unexpected demands upon others, progressively degrading the capacity of the broader system to maintain normal operations.
Cybersecurity must therefore be understood as something substantially broader than the protection of individual computers against malicious intrusion. It encompasses the preservation of essential societal functions when components of the digital infrastructure become unreliable.
The Aviation Safety Parallel
The aviation industry provides a particularly relevant framework for understanding the emerging infrastructure problem. Aviation safety emerged from decades of investigation into accidents involving equipment failures, human error, inadequate procedures, organizational deficiencies, and interactions among multiple contributing factors.
One of the most important principles of modern aviation safety is the recognition that catastrophic outcomes frequently develop through the interaction of failures that might individually appear manageable. Effective safety management consequently emphasizes redundancy, independent verification, fault tolerance, contingency planning, and the identification of latent organizational vulnerabilities.
These principles are equally relevant to national digital infrastructure. A cyberattack against a single organization becomes considerably more consequential when numerous essential services depend upon the targeted organization. Similarly, a software failure becomes a systemic threat when alternative operational capabilities are insufficient or rely upon the same compromised infrastructure.
The objective should not be limited to preventing every conceivable technological failure. It must also include ensuring that inevitable failures do not escalate into unacceptable operational consequences.
Applying established safety-engineering principles to cybersecurity would require organizations to examine not merely the probability of an intrusion but also the severity of its potential consequences, the independence of backup systems, the reliability of recovery procedures, and the capacity of personnel to continue essential operations under degraded conditions.
Artificial Intelligence and the Changing Threat Environment
The rapid development of artificial intelligence introduces another dimension to the global cybersecurity environment. Artificial intelligence can strengthen defensive capabilities through automated anomaly detection, accelerated analysis of security events, and the identification of vulnerabilities within complex networks.
However, similar technological advances can assist malicious actors in developing more convincing fraudulent communications, identifying vulnerable systems, automating elements of hostile activity, and accelerating the analysis of information acquired through unauthorized access.
The resulting environment is characterized by increasingly sophisticated competition between defenders and attackers. Security procedures that were adequate against traditional threats may become less effective as automation increases the speed, scale, and adaptability of malicious operations.
There is no publicly established evidence that artificial intelligence was employed in the reported NCIC intrusion. Its broader relevance lies in the changing technological environment within which governmental and commercial security organizations must defend increasingly complex digital infrastructure.
National Security Beyond Conventional Military Authority
For much of modern history, national security was principally associated with territorial defense, military readiness, intelligence collection, and the protection of governmental institutions against physical threats. Digital dependency has fundamentally expanded that definition.
A nation’s ability to maintain public order, distribute energy, administer justice, process financial transactions, coordinate air transportation, and deliver medical services increasingly depends upon infrastructures that may be vulnerable to interference without the deployment of conventional military forces.
Indeed, a sufficiently extensive disruption of essential digital services could impose significant economic and administrative consequences without a single physical attack against national territory. The destabilizing effects could be magnified by uncertainty concerning the source, duration, and reliability of information available to affected organizations.
These vulnerabilities are not confined to the United States. The international nature of software supply chains, communications networks, cloud services, and financial infrastructure means that technological failures originating within one country can affect organizations worldwide.
The protection of digital infrastructure has consequently become a central element of national sovereignty, economic security, and international stability.
The Growing Importance of Operational Resilience
Preventing unauthorized access remains an indispensable cybersecurity objective. However, operational resilience demands considerably more than the installation of defensive software or the periodic remediation of identified vulnerabilities.
Essential organizations must maintain the ability to independently validate critical information, detect unauthorized modifications, preserve reliable recovery records, and continue essential operations when their primary technological capabilities are degraded. Backup infrastructures must be sufficiently isolated to avoid simultaneous compromise through shared dependencies.
For criminal justice organizations, this includes the ability to establish the reliability of records subsequently used to justify detention, arrest, or other consequential law enforcement decisions. Following a suspected compromise, restoration of system availability alone may be insufficient if the accuracy of the underlying information cannot also be established.
Institutional transparency is another important component of resilience. Agencies responsible for essential infrastructure must communicate sufficiently with dependent organizations to enable informed operational decisions during periods of uncertainty, while protecting sensitive investigative and security information.
The ability to restore public confidence depends not simply upon assurances that a system is functioning, but upon demonstrable evidence that it is functioning correctly.
Another Failure, Another Warning
The apparent intrusion into the National Crime Information Center must ultimately be evaluated according to the technical findings of the FBI’s investigation. Its full operational significance cannot be determined until the nature and extent of the unauthorized access have been established.
Nevertheless, the incident already raises an important question that extends beyond the circumstances of any individual cybersecurity investigation: Has the development of global technical infrastructure outpaced the development of the mechanisms necessary to protect its operational integrity?
Modern society has invested extraordinary resources in expanding the capabilities, speed, convenience, and interconnectedness of its technological systems. These investments have transformed virtually every component of civilization. Yet the increasing concentration of essential functions within interconnected digital environments demands an equally extraordinary investment in resilience, independent verification, redundancy, and institutional preparedness.
The succession of cybersecurity incidents and technological disruptions should not be dismissed merely because their origins may differ. Their collective significance lies in what they reveal about the vulnerability of the infrastructure upon which contemporary civilization depends.
The fundamental concern is no longer simply whether an individual government database can be breached. It is whether governments and societies can continue functioning safely when the technological infrastructure supporting their most essential activities can no longer be trusted.
Sources
CNN — The FBI Was Hacked Again, This Time the Breach Targeted Its Crime Database, November 20, 2026.
Reuters — FBI’s Criminal Information Database Hacked, CNN Reports, November 21, 2026.
Forbes — FBI Reportedly Hacked Again: Apparent Breach Hits NCIC Crime Database, November 21, 2026.